Annual Compliance Programme in Banks: Building the Calendar (IIBF BCP)
Every bank builds its compliance work around one document: the annual compliance programme in banks. It is not a checklist bolted on at year-end — it is the risk-based plan that decides which branches get tested, which regulations get sampled, and how often the compliance function reports to the board. For a candidate preparing for the IIBF Banking Compliance Professional (BCP) certification, understanding how this programme is built, approved and executed matters, because examiners test the mechanics, not just the definition.
This article walks through how the compliance function assembles the programme from the universe of applicable statutes and master directions, how it risk-ranks each obligation, how the testing calendar is structured across the year, and how the loop closes with the board through the quarterly compliance report and the annual compliance certificate.
📋 Building the Compliance Universe and Owner Mapping
The starting point of any annual compliance programme in banks is the "compliance universe" — an exhaustive inventory of every statute, RBI master direction, master circular, and internal policy that applies to the bank's activities. This universe spans deposit-taking rules, KYC and AML obligations, lending restrictions, priority sector norms, foreign exchange regulations, and conduct requirements. Nothing on the list is optional to record, even where the risk looks low.
Each obligation is then mapped to the business unit that owns it operationally — retail banking, credit, treasury, trade finance, or operations. This ownership matters because the compliance function does not execute the control itself; it tests whether the business unit's control is working. A lending restriction sits with the credit department, while a KYC obligation sits with branch operations. Chapters such as Loans and Advances Regulatory Restrictions and Guarantees, Acceptances and Finance to NBFCs map directly onto obligations pulled into this universe.
Without a complete, current universe, the programme collapses — you cannot risk-rank or schedule testing for an obligation nobody recorded. Refreshing the universe at least once a year, and whenever a new regulation or product appears, keeps the base honest.
🎯 Risk-Ranking Obligations and Setting Testing Frequency
Once every obligation is on the universe, the compliance function scores each one on two axes: impact of a breach (financial loss, customer harm, regulatory penalty, reputational damage) and likelihood of a breach (control maturity, past incidents, staff turnover, process complexity). The resulting rating decides how often that obligation gets tested — high-impact, high-likelihood items go on a monthly or transaction-level cycle; stable, low-risk obligations may only need annual or biennial testing.
This step is what turns a static universe into a working annual compliance programme in banks: risk-ranking allocates a scarce compliance team's hours to where a breach would actually hurt. Obligations tied to large exposures, IRAC classification, or interest-rate pass-through are usually rated high because the cost of a miss is large and immediate. Chapters like Large Exposures and Exposure Norms and IRAC Norms and Wilful Defaulters sit in the high-frequency testing band for most banks.
💡 Exam Tip: Remember the two-axis logic — impact times likelihood — not just "high risk gets tested more". Examiners often probe whether a low-impact, high-likelihood item can still outrank a high-impact, low-likelihood one on the calendar.
🗓️ The Testing Calendar: On-Site, Thematic and Off-Site Mix
The programme is executed through a testing calendar that blends three techniques. On-site branch testing has compliance staff sampling files and transactions at branches — useful for KYC, cash transaction reporting, and documentation checks. Thematic reviews go deep on one regulatory topic across multiple branches, such as interest-rate reset compliance on floating-rate retail loans. Off-site data analytics uses core banking extracts to test large populations for exceptions without a branch visit, and is the fastest-growing part of most calendars because of the volume it can cover.
Monthly testing typically covers the highest-risk obligations — cash limits, suspicious transaction monitoring, interest computation. Quarterly testing covers a wider thematic sweep and closes with the quarterly compliance report to the board or its audit/risk committee. The calendar is a working document; the compliance function revises it mid-year if a new circular, a supervisory finding, or an internal incident changes the risk picture for any obligation.
🤝 Coordinating the Three Lines of Defence
A bank runs three lines of defence: the business unit that owns and operates the control (first line), compliance and risk that independently test and challenge it (second line), and internal audit that provides independent assurance over both (third line). A well-run annual compliance programme in banks is built in explicit coordination with internal audit and risk management so the three lines do not duplicate testing on the same obligation in the same period.
In practice this means compliance and internal audit exchange their annual plans before finalisation, flag overlapping scope, and either split coverage by branch and period or agree that one function's testing can be relied upon by the other, subject to quality review. Risk management feeds its own RCSA outputs and incident data into the risk-ranking exercise rather than running a separate cycle. This coordination is itself reviewed by the board and audit committee, since duplicated testing wastes resources while gaps between the three lines leave obligations untested.
⚠️ Common Mistake: Treating compliance testing and internal audit as fully separate exercises. Examiners expect you to know overlap is actively managed, not tolerated as three independent processes running in parallel.
📈 Observations, the Compliance Certificate and the CCO's Role
Every testing activity produces observations, and each is tracked to closure with a documented root cause — process gap, training gap, system limitation, or wilful override. A repeat breach of the same root cause across cycles is escalated with a higher severity rating and a tighter closure timeline, because repetition signals the first fix did not address the actual cause.
The programme reports upward on two rhythms: a quarterly compliance report summarising testing coverage, open and closed observations, and emerging risks, and an annual compliance certificate presented to the board confirming the programme was executed as approved. The board and its audit committee approve this programme at the start of each cycle and receive both the quarterly reports and the year-end certificate — this approval-and-certification loop is what makes the programme board-owned, not just a compliance-department checklist.
The Chief Compliance Officer running this programme is expected to be independent of business-line pressure, hold a minimum tenure to avoid short-termism, and report functionally to the board or its committee rather than to business heads. Supervisory findings from RBI inspections feed directly into next year's risk-ranking, often elevating obligations where the regulator flagged gaps. See Interest Rates on Advances for a related lending obligation that regularly appears on this calendar.
| Programme Element | Typical Frequency | Reports To | Board-Approved |
|---|---|---|---|
| High-risk obligation testing (cash, STR, interest computation) | Monthly | CCO / Compliance Committee | ✅ |
| Thematic review (one regulation, multiple branches) | Quarterly | Audit Committee | Yes |
| Off-site data analytics sweep | Monthly / Continuous | CCO | Yes |
| Quarterly compliance report | Quarterly | Board / Audit Committee | Yes |
| Annual compliance certificate | Annual | Board | Yes |
| Ad hoc testing without documented root cause | Not part of programme | — | ❌ |
📌 Remember: The calendar is not fixed for the year — supervisory findings and repeat breaches can trigger a mid-year revision to testing frequency for specific obligations.
Two feeds keep the universe current every year: a new product's compliance sign-off, covered in new product approval compliance in banks, and every fresh RBI circular, triaged and slotted into the calendar as explained in regulatory change management in banks. Digital lending obligations follow the same path — see compliance obligations in digital lending. For the governance backdrop on why independent testing exists, read the sibling piece on moral hazard in banking. RBI's own supervisory guidance on the compliance function and CCO role, published at rbi.org.in, is the primary source to read alongside this summary.
🧠 Practice MCQs: Annual Compliance Programme in Banks
Q1. The compliance function builds its testing calendar primarily by risk-ranking obligations on which two factors? (a) Cost of testing and staff availability (b) Impact of breach and likelihood of breach (c) Branch size and region (d) Regulator seniority
Answer: (b) — Impact of breach and likelihood of breach jointly decide the testing frequency, not either factor alone.
Q2. Who formally approves the annual compliance programme before the testing cycle begins? (a) The Chief Compliance Officer alone (b) Internal audit (c) The board or its audit committee (d) The regulator
Answer: (c) — Board or audit committee approval at the start of the year makes the programme a governance-owned document.
Q3. A compliance observation with the same root cause recurring across two testing cycles should be: (a) Closed automatically since it was reported once (b) Escalated with tighter closure timelines (c) Removed from the tracker (d) Reassigned to internal audit only
Answer: (b) — Repeat breaches on the same root cause signal an ineffective earlier fix and are escalated, never auto-closed.
Q4. Which technique in the testing calendar is best suited to testing large transaction populations without a branch visit? (a) On-site branch testing (b) Thematic review (c) Off-site data analytics (d) Annual certification
Answer: (c) — Off-site data analytics uses core banking extracts to cover large populations remotely, unlike on-site sampling.
Q5. Coordination between compliance, risk and internal audit on the annual programme exists mainly to: (a) Increase total audit hours (b) Avoid duplicate testing of the same obligation across the three lines of defence (c) Remove the need for a compliance certificate (d) Shift ownership of controls to internal audit
Answer: (b) — The three lines coordinate so the same obligation is not independently retested in the same period, keeping coverage efficient.
Want chapter-wise mock tests with 100+ MCQs? Start practising free →
What is the annual compliance programme in banks?
It is the risk-based plan, approved by the board at the start of the year, that lists every applicable statute, master direction and internal policy, ranks each on impact and likelihood of breach, and sets a testing frequency and calendar for the compliance function to verify each control.
How often is the compliance testing calendar reviewed?
The base calendar is set annually, but it is a living document — a new circular, a supervisory finding, or a repeat breach can trigger a mid-year revision to the testing frequency for specific obligations.
Why does the programme coordinate with internal audit and risk management?
Because all three sit in the three lines of defence and test overlapping obligations; without coordination on scope and timing, the same control gets tested twice while another goes untested for the year.
What does the Chief Compliance Officer certify to the board each year?
The CCO presents an annual compliance certificate confirming the approved programme was executed as planned and summarising the bank's overall compliance posture, supported through the year by quarterly compliance reports.
🏁 Conclusion: Make the Programme Exam-Ready
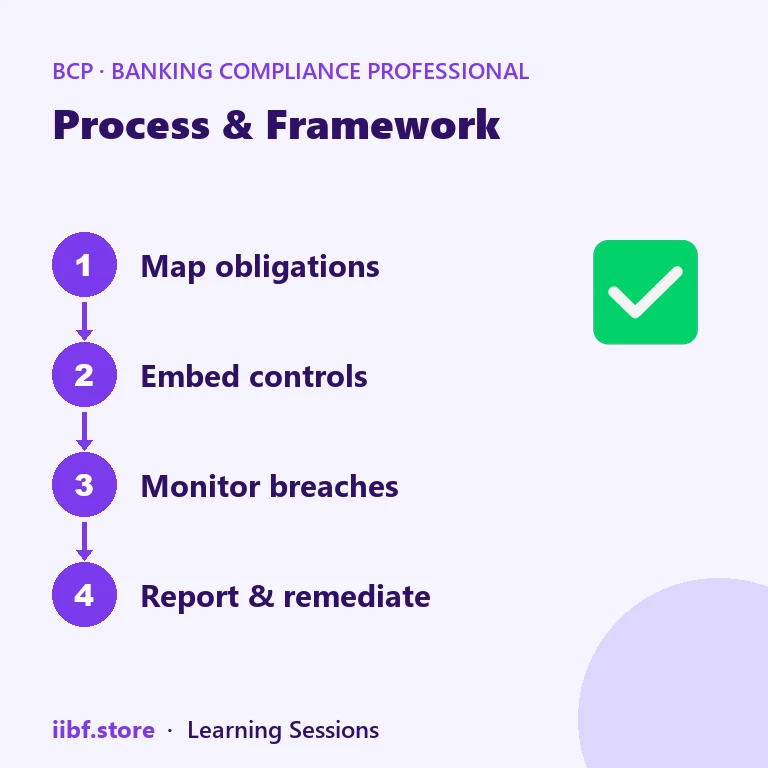
For the BCP exam, remember the sequence: universe, ownership mapping, risk-ranking, calendar, execution mix, three-lines coordination, observation closure, and board certification. Every part of the annual compliance programme in banks connects a regulatory obligation to a tested control and a board-visible outcome — memorising the sequence, not just the definition, is what separates a pass from a top score. Practise this with topic-wise questions at iibf.store/tests, and browse more BCP reads on the Banking Compliance Professional tag hub.
Practice this topic
Take a free mock test, download chapter PDFs, or watch a video class — all included on iibf.store.
Keep reading